CVE-2026-63082 - Perfect Support Ticketing System 1.7 Broken Access Control via Agent Assignment
A GitHub repository version of this disclosure can be read here: CVE-2026-63082.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-63082 |
| Severity | 5.3 Medium (CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N) 5.4 Medium (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N) |
| Date Published | 2026-07-17 |
| Software Name | Perfect Support Ticketing & Document Management System |
| Affected Version(s) | 0 through 1.7 |
| Software Link | https://codecanyon.net/item/perfect-support-ticketing-document-management-system/32094844 |
| Vendor | Ultimate Fosters |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran), Shahrul Nizam Bin Shahrin |
Description
Perfect Support Ticketing & Document Management System through 1.7 contains a broken access control vulnerability that allows authenticated attackers with Agent-level privileges to manipulate the Support Agent assignment field of tickets by bypassing intended authorization checks. Attackers can add or remove any user, including Superadmin accounts, from the Support Agent field of any ticket to which they are assigned, circumventing role-based access controls.
Proof-of-Concept
1. As a prerequisite, ensure you are having access to an account with Agent privileges and an active support ticket is assigned to the target Agent (e.g., assigned by a Superadmin). Log in to the application using an account with Agent privileges.
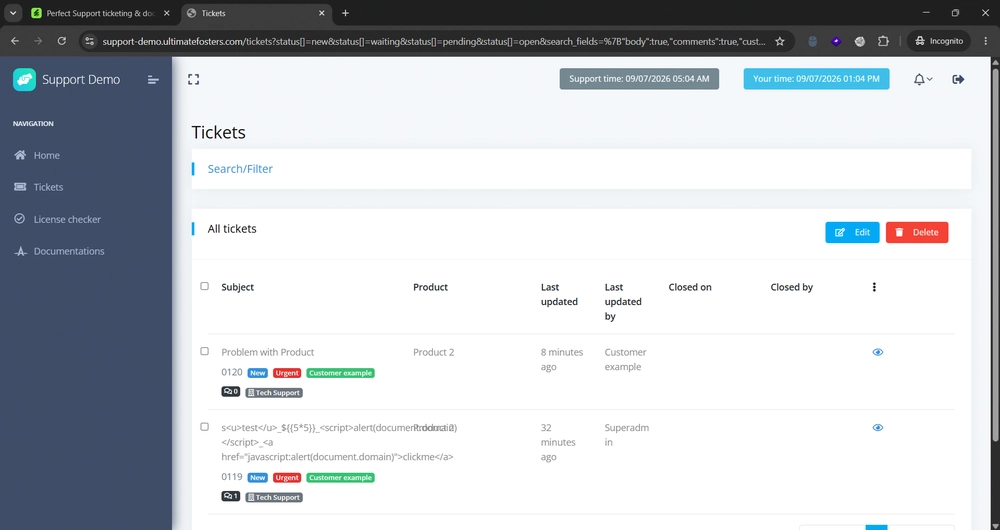
2. Open the assigned support ticket from the agent dashboard.
3. Locate the Support Agent assignment field on the ticket management interface. Notice that despite having lower privileges, the Agent has full modification rights over this field.
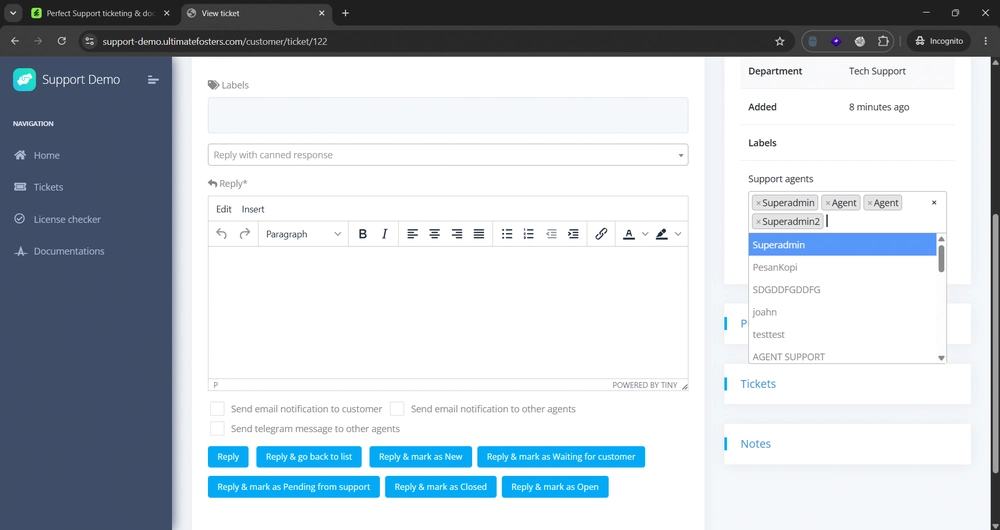
4. Interact with the field to arbitrarily add or remove assigned users, including high-privileged Superadmin accounts, thereby breaking intended access controls and privilege boundaries.
Timeline
- 9 July 2026: Initial discovery of a vulnerability in Perfect Support Ticketing System v1.7 using their Live Demo instance. We sent a full email report directly to VulnCheck.
- 15 July 2026: VulnCheck replied stating that following an initial triage, they were unable to locate a clear security reporting method to Ultimate Fosters, and they supported our decision to proceed with a public disclosure.
- 16 July 2026: Received the reserved CVE IDs for the vulnerability from VulnCheck. We published a public disclosure in my CVE-Disclosures repository on GitHub. VulnCheck then officially published CVE-2026-63082 later that day.
- 17 July 2026: Published this blog post.
See you in the next hack.
@aaronamran
July 2026