CVE-2026-66030 - Ekushey Project Manager CRM 5.0 Stored XSS via Client Name Field
A GitHub repository version of this disclosure can be read here: CVE-2026-66030.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-66030 |
| Severity | 5.1 Medium (CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:N/VA:N/SC:L/SI:L/SA:N) 5.4 Medium (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N) |
| Date Published | 2026-07-27 |
| Software Name | Ekushey Project Manager CRM |
| Affected Version(s) | 0 through 5.0 |
| Software Link | https://codecanyon.net/item/ekushey-project-manager-crm/9492104 |
| Vendor | Creativeitem |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran) |
Description
Ekushey Project Manager CRM through version 5.0 contains a stored cross-site scripting vulnerability that allows authenticated client users to inject arbitrary HTML and JavaScript by entering malicious payloads into the Ticket Title field on the Create New Ticket page. Attackers can craft and store malicious scripts that execute in the browser sessions of Staff or Administrator users who view the Client Support page where ticket titles are rendered unsanitized.
Proof-of-Concept
1. Only the Client users are able to create new tickets. Authenticate as a lower-privileged Client user, navigate to the Create New Ticket page, and set the Ticket Title field to the following XSS payload. Fill in any required remaining fields with valid data and submit the form:
<u>Ticket Title</u><script>alert("Client Name Stored XSS")</script>
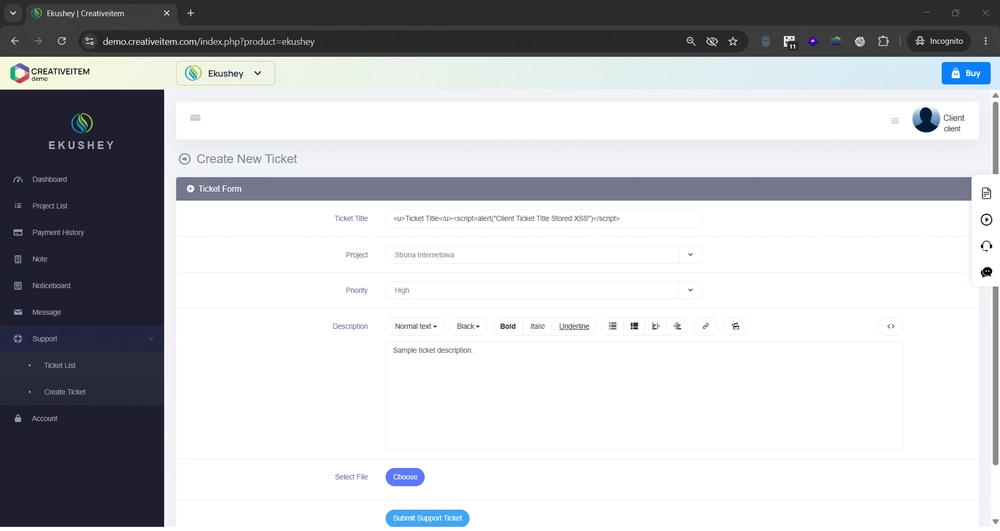
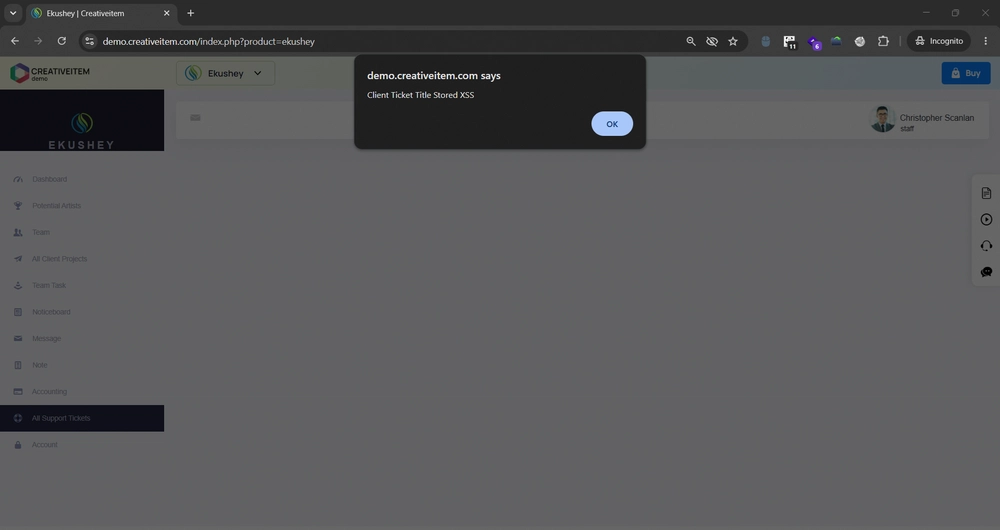
2. Log out of the Client account and log in as a Staff user. Navigate to All Support Tickets in the left panel. The payload executes immediately upon rendering the ticket summary table.
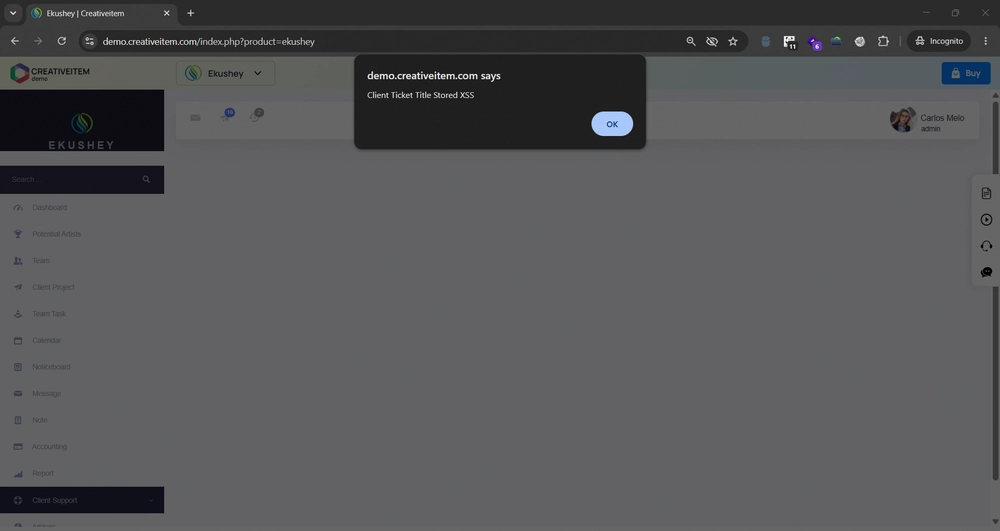
3. Authenticate as an Admin user and navigate to the Client Support page. The stored XSS triggers identically within the Admin control panel.
Timeline
- 23 July 2026: This vulnerability in Ekushey Project Manager CRM v5.0 was initially discovered using their live demo instance.
- 24 July 2026: I submitted a complete report to VulnCheck.
- 25 July 2026: Following an initial triage, VulnCheck confirmed they were unable to locate a security reporting mechanism for Creativeitem. Consequently, they supported the decision to proceed with public disclosure and reserved a CVE ID for this vulnerability.
- 26 July 2026: I published a public disclosure in my CVE-Disclosures repository on GitHub.
- 27 July 2026: VulnCheck then officially published CVE-2026-66030.
- 28 July 2026: I published this blog post.
See you in the next hack.
@aaronamran
July 2026