CVE-2026-70560 - Ultimate POS Stored XSS via First Name Field in Leave Notifications
A GitHub repository version of this disclosure can be read here: CVE-2026-70560.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-70560 |
| Severity | 4.8 Medium (CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:A/VC:L/VI:L/VA:N/SC:L/SI:L/SA:N) 5.4 Medium (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N) |
| Date Published | 2026-08-12 |
| Software Name | Ultimate POS |
| Affected Version(s) | 0 through 7.2 |
| Software Link | https://codecanyon.net/item/ultimate-pos-stock-management-point-of-sale-application/21216332 |
| Vendor | Ultimate Fosters |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran) |
Description
Ultimate POS (Stock Management & Point of Sale) contains a stored cross-site scripting vulnerability that allows low-privileged authenticated attackers to inject arbitrary HTML and script markup by setting a malicious payload in the user first-name field during account creation. Attackers with a low-privileged role such as Cashier can submit a leave request through the HRM/Leave module, causing the unsanitized first-name markup to execute in the browser session of any higher-privileged user who views the leave-application notification pane, enabling cross-user session compromise within the admin origin.
Proof-of-Concept
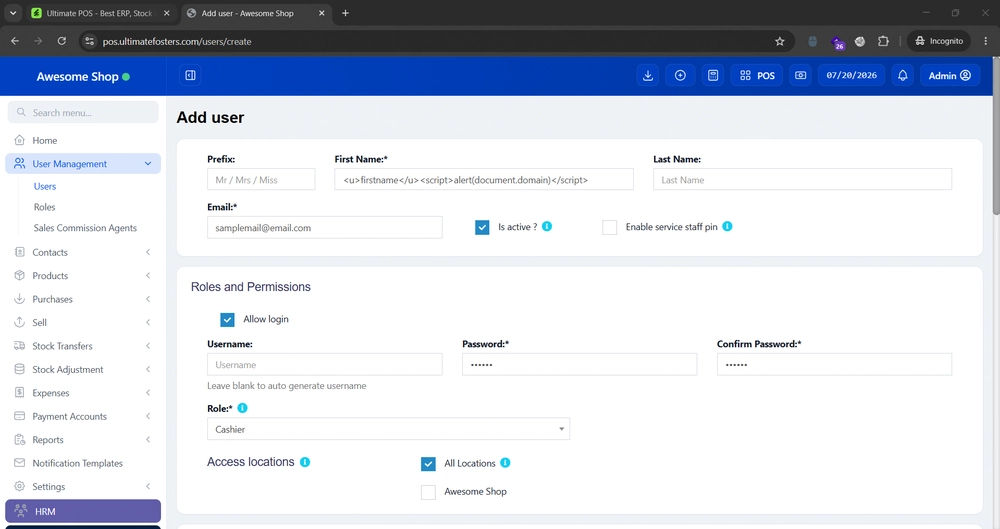
The live demo of Ultimate POS v7.2 does not allow self-registration without authenticating first. For the purpose of this PoC, log in as the demo admin user and create a new user account. Insert the following XSS payload into the user's First Name field, filling the remaining fields with arbitrary test data:
<u>firstname</u><script>alert(document.domain)</script>
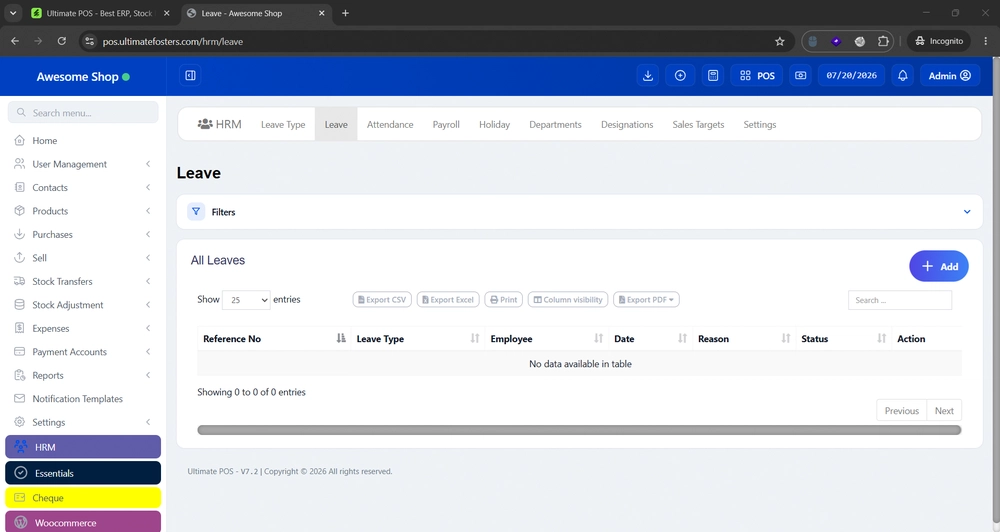
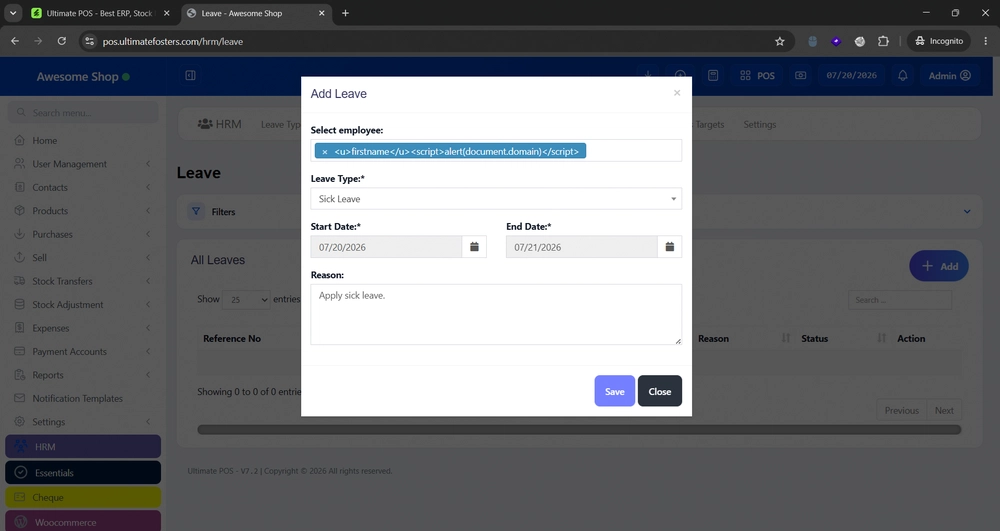
2. Once the user is created, navigate to the HRM module and add a leave request on behalf of that user. Select the newly created employee, fill in any required fields with dummy data, and save the changes.
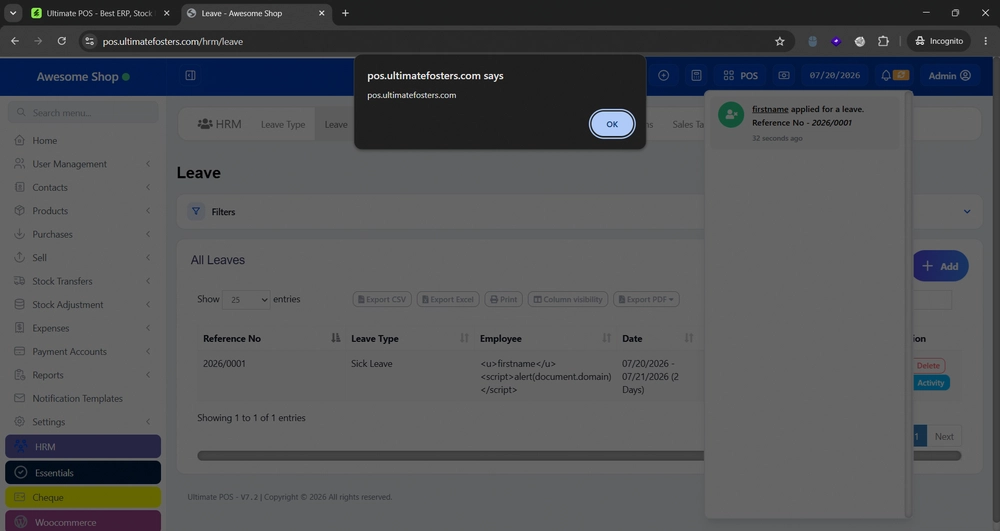
3. When an administrator opens or views the leave request notification, the stored XSS payload executes automatically due to improper input sanitization and unescaped rendering.
Timeline
- 3 August 2026: This vulnerability in Ultimate POS v7.2 was initially discovered using their live demo instance. I submitted a complete report to VulnCheck.
- 07 August 2026: Following an initial triage, VulnCheck confirmed they were unable to locate a security reporting mechanism for Creativeitem. Consequently, they supported the decision to proceed with public disclosure and reserved a CVE ID for this vulnerability. I published a public disclosure in my CVE-Disclosures repository on GitHub.
- 12 August 2026: VulnCheck then officially published CVE-2026-70560.
- 14 August 2026: I published this blog post.
See you in the next hack.
@aaronamran
August 2026