DOM XSS in The UK Intelligence Community UI Kit
I have been contemplating whether I should write a blog post about this, because I usually do not include vulnerabilities discovered for CVE assignment purposes in my 'Ethical Hacking' blog. I have long been interested in intelligence agencies and things related to espionage, hence I made it a goal, for the sake of personal achievement, to hunt and responsibly disclose valid cyber vulnerabilities in intelligence agencies where allowed and possible.
I cannot confirm whether MI6 has an actual Vulnerability Disclosure Program, but in the context of this blog, I reported the DOM XSS, discovered on a local setup, based on the SECURITY.md file here.
I will skip the technical replication details in this blog, since all the information needed can be discovered in my CVE disclosure here. Now you might be wondering, how did I even discover the existence of this GitHub repository? Let me answer that question. As I was searching for more CVE-eligible targets on open-source software to increase my CVE count, I realised that many big organisations or companies have their own GitHub pages with many repositories. So I went to search for things like 'Microsoft GitHub', 'Nvidia GitHub' and many others. Eventually, I came across the MI6 GitHub page.
I checked through their repositories, and identified which ones are eligible for CVEs. In my mind, I thought it would be crazy if I could find at least one vulnerability in such a well-known agency. After some hours of searching and with AI assistance, I found a sink where DOM XSS pops.
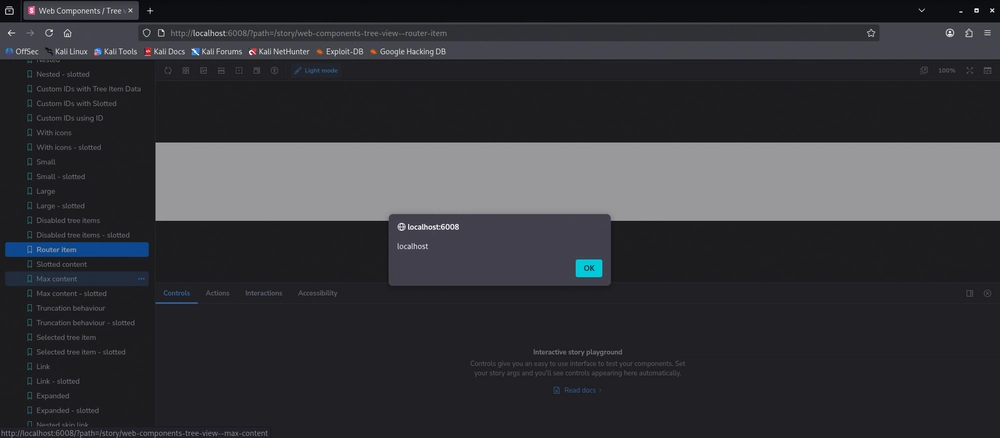
I immediately sent a detailed report to the email address provided in the SECURITY.md file on 27 September 2026. Apparently, the maintainers have not replied until now. So once I discovered that the vulnerability had been patched, I took note of the patch commit on GitHub, and applied for a CVE from VulnCheck on 19 October 2026. VulnCheck assigned CVE-2026-112290 to this vulnerability.
See you in the next hack.
@aaronamran
November 2026