Motorola Solutions Pre-Authentication PII Leak
I could have written a detailed blog post explaining exactly how I found this vulnerability, but I am lazy. You will understand why as you read on. Motorola Solutions hosts an official Responsible Vulnerability Disclosure Program here.
As usual, after an hour of reconnaissance, I found a few interesting things worth further investigation. However, one of them immediately caught my eye. Feel free to zoom into the screenshot below and test yourself to see if you can find it. As a disclaimer, this specific vulnerability isn't guaranteed to exist in other companies because it heavily depends on their unique configuration. This is exactly why actual, hands-on testing is required.
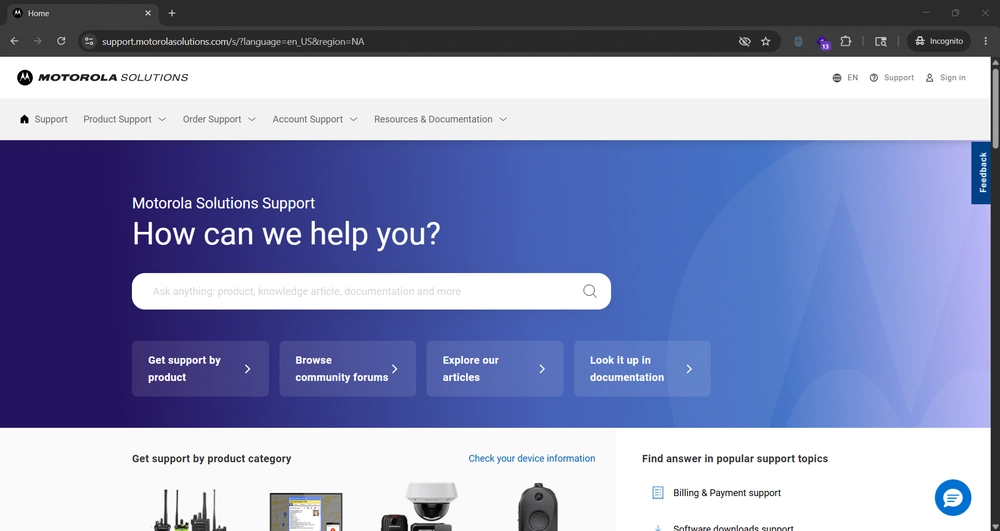
If you can spot the massive giveaway hinting at the vulnerability in the screenshot above, you have sharp eyes and have clearly spent time hunting in the real world, rather than spending most of your time in some fictional (and intentionally vulnerable) lab environment.
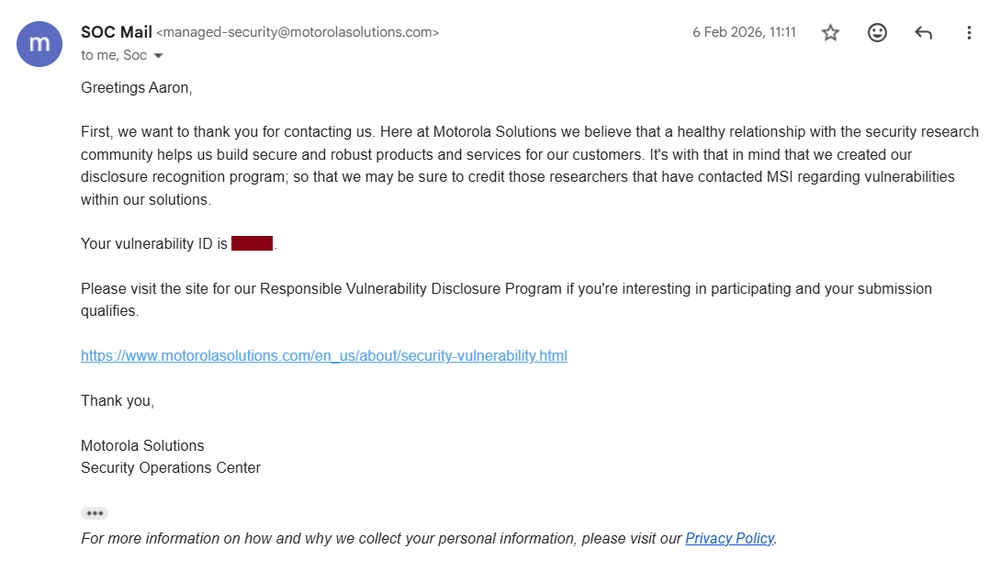
Once I identified the security flaw and successfully exploited it, I reported all the necessary details to their cybersecurity team on 6 February 2026 at 9:58 AM. I distinctly remember rushing to submit that email because I had a work meeting scheduled at 10:00 AM. If you thought I was going to attend the meeting first and submit my disclosure report later, sorry, but no. Finding vulnerabilities is highly addictive to me; I need to get them out of my system before my mind can clear up space for anything else. Later that same day, at 11:11 AM, I received a formal acknowledgement email from the Motorola Solutions Security Operations Center team confirming my submission had been received.
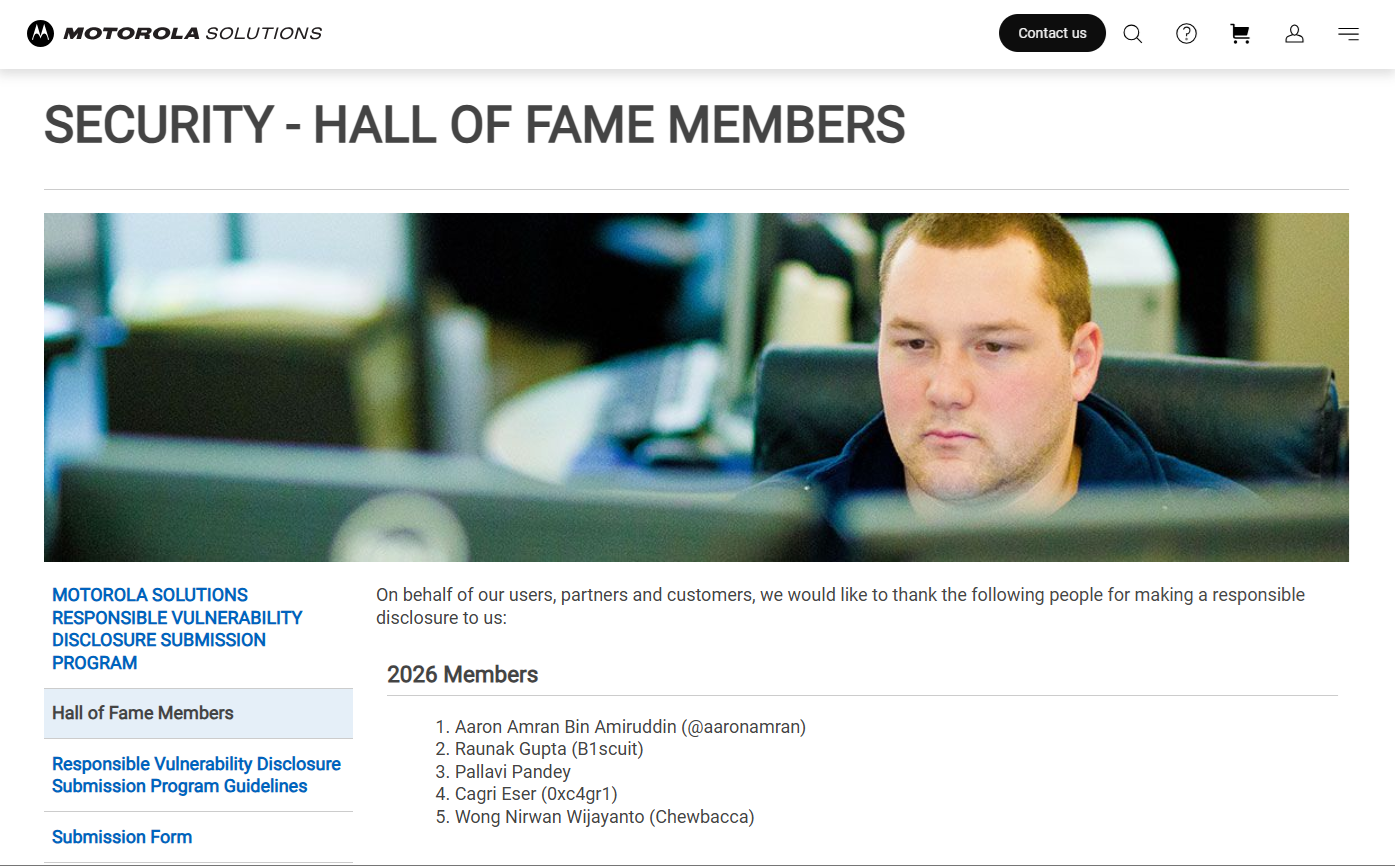
After that, everything went completely quiet. I didn't receive any further emails or updates. Because of the radio silence, I assumed my vulnerability hadn't been accepted, so I never bothered to check Motorola's Security Hall of Fame to see if my name would ever appear.
Then, out of nowhere on the evening of 19 May 2026, I stumbled upon Raunak Gupta's celebratory LinkedIn post about his name being listed in Motorola's Hall of Fame. As I glanced at it, my eyes immediately caught a name that looked remarkably familiar. Wait a minute... it was actually me! I had no idea I was listed in the 2026 Hall of Fame. Had Raunak not shared his achievement on LinkedIn, and had it not popped up on my feed, I would still be completely in the dark. Fate works in mysterious ways.
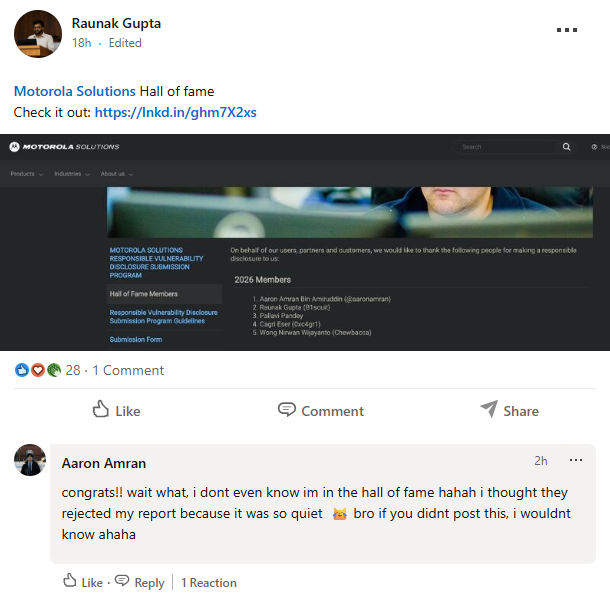
Ultimately, the main reason I am not diving deep into the technical exploits that leaked tons of user PII on Motorola's website is that doing so requires explicit permission for full public disclosure, as stated in the excerpt of their VDP guidelines below.
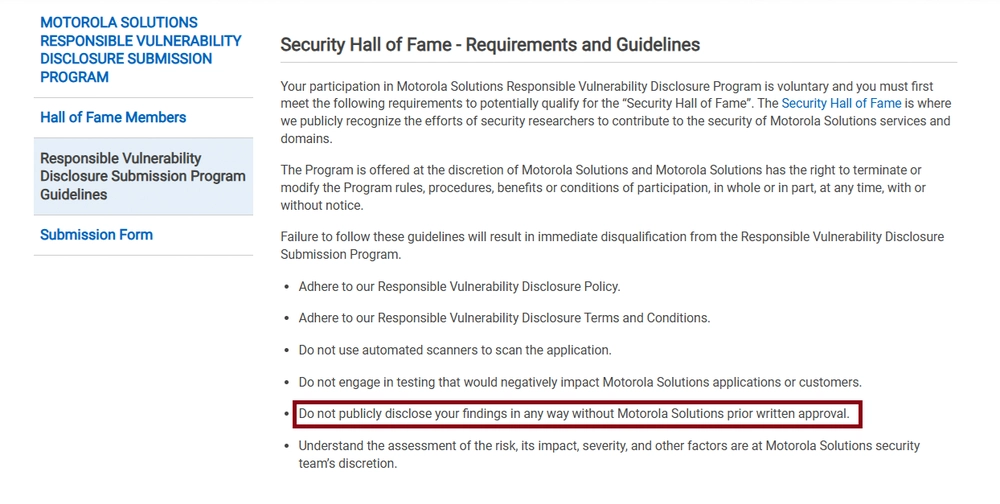
Given that they didn't bother updating me after their initial acknowledgement, I highly doubt they would reply to any subsequent emails requesting disclosure approval.
See you in the next hack.
@aaronamran
May 2026